From Zero Trust Foundations to Post-Quantum Readiness
A Practitioner's Handbook for Securing Cloud at Scale
Not a checklist. Not a blog post. A 150-page structured reference with 12 decision tables, 5 deployable Terraform labs, and an 18-chapter framework used to secure platforms serving millions of users.
7-day money-back guarantee. No questions asked.
The Cloud Security
ARCHITECT'S
HANDBOOK
Afaan Bilal
Comprehensive Chapters
Pages
Decision Tables
Hands-On Labs
What Makes This Different
Most technical books don't have a curated reference appendix, deployable labs, or a concrete action plan. This one does.
5 Deployable Labs
Complete Terraform and GitHub Actions labs, each with step-by-step setup, a "what to verify" checklist, and cleanup instructions.
- ›Zero-Trust VPC architecture
- ›DevSecOps pipeline with automated IaC and image scanning
- ›AWS Identity Center SSO configuration
- ›GuardDuty alerting
- ›S3 encryption enforcement with AWS Config
12 Architectural Decision Tables
A curated reference appendix designed to be the resource you return to when making real decisions: which IaC tool fits your stack, when to use OPA vs. SCPs, how to split SIEM and SOAR responsibilities, how to manage mTLS certificate lifecycles across service mesh and non-mesh environments.
Designed to stay open on your second monitor.
The 30-Day Action Plan
Finished the book and not sure where to start? The conclusion includes a concrete 30-day action plan — specific tools and commands, prioritized by impact, with chapter references for each action.
Days 1-7
Visibility
Days 8-14
Identity hardening
Days 15-21
Eliminate the obvious risks
Days 22-30
Build the foundation
From the Book
The writing quality is worth the price. Here's a sample.
“A virtual machine has one operating system and one workload. A Kubernetes cluster has one control plane managing hundreds of workloads, each with its own network identity, filesystem access, and privilege level — all sharing the same underlying nodes. The attack surface is not just the workloads; it is the orchestrator itself.”
Chapter 7
Container & Kubernetes Security
“Most compliance programs are built around a calendar, not a threat model. Auditors arrive once a year, review evidence of controls that were in place on a handful of sampled days, and issue a report. The problem is that your attack surface does not pause between audits.”
Chapter 10
Compliance & Governance
“The most dangerous sentence in cloud security is: "AWS handles that."”
Chapter 2
Shared Responsibility Model
Newly published — be among the first to leave a review.
Who This Is For
This handbook knows exactly who it's for — and has structured itself accordingly.
| Role | Priority Chapters | Why |
|---|---|---|
| CISO / Security Director | 1, 2, 12, 13 | Threat landscape, responsibility model, roadmap, metrics |
| Cloud Security Architect | 3, 4, 5, 6, 15 | Identity, network, data, compute, advanced patterns |
| DevSecOps Engineer | 7, 8, 11, Appendix A | Container security, IaC, CI/CD, hands-on labs |
| Compliance / GRC | 2, 10, 11, 13 | Shared responsibility, governance, compliance frameworks |
| Cloud Engineer / SRE | 4, 6, 8, 9 | Network, compute, IaC, monitoring and incident response |
| Security Analyst / SOC | 9, 10, 11 | Monitoring, threat detection, incident response |
| Application Developer | 3, 7, 15 | IAM, application security, advanced API and GraphQL |
CISO / Security Director
Chapters: 1, 2, 12, 13
Threat landscape, responsibility model, roadmap, metrics
Cloud Security Architect
Chapters: 3, 4, 5, 6, 15
Identity, network, data, compute, advanced patterns
DevSecOps Engineer
Chapters: 7, 8, 11, Appendix A
Container security, IaC, CI/CD, hands-on labs
Compliance / GRC
Chapters: 2, 10, 11, 13
Shared responsibility, governance, compliance frameworks
Cloud Engineer / SRE
Chapters: 4, 6, 8, 9
Network, compute, IaC, monitoring and incident response
Security Analyst / SOC
Chapters: 9, 10, 11
Monitoring, threat detection, incident response
Application Developer
Chapters: 3, 7, 15
IAM, application security, advanced API and GraphQL
Taken directly from the book's conclusion — the role table that maps each reader to their highest-value chapters.
The Cloud Security
ARCHITECT'S
HANDBOOK
Afaan Bilal
Designed for Modern Architects
Whether you're designing a new cloud environment or securing existing infrastructure, this handbook provides the knowledge and patterns you need.
Battle-Tested Patterns
Real architectures from organizations securing millions of transactions daily.
Future-Ready
Coverage of emerging threats including AI security and post-quantum cryptography.
Implementation-Focused
Code examples, IaC templates, and deployment strategies you can use immediately.
Multi-Cloud Native
Security patterns for AWS, Azure, GCP, and hybrid cloud environments.
Complete Book Structure
18 chapters organized into 6 comprehensive parts, covering everything from foundational concepts to implementation and advanced future-proofing strategies.
CH.01Cloud Security Fundamentals
CH.02Shared Responsibility Model
CH.03Identity & Access Management (IAM)
CH.04Network Security Architecture
CH.05Data Protection & Encryption
CH.06Compute Security
CH.07Container & Kubernetes Security
CH.08Infrastructure as Code (IaC) Security
CH.09Monitoring & Incident Response
CH.10Compliance & Governance
CH.11Cost-Optimized Security
CH.12Implementation Roadmap
CH.13Security KPIs and Metrics
CH.14Securing Generative AI & LLMs
CH.15Advanced API Security
CH.16Multi-Cloud Security Strategy
CH.17Automating Remediation (SOAR)
CH.18Secrets Management & Machine Identity
Also Included: Introduction, Conclusion with 30-Day Action Plan, 5 Practical Labs (Zero-Trust VPC, DevSecOps Pipeline, AWS Identity Center SSO, GuardDuty Alerting, S3 Encryption Enforcement), Appendix B with 12 Decision Tables, and a comprehensive Glossary.
Inside the Handbook
Sample content showing the depth and practical focus of this handbook
Zero Trust Architecture Pattern
A practical implementation guide for identity-first security, including architecture diagrams and configuration examples for AWS, Azure, and GCP.
"Identity is the control plane. Every access decision—whether from users, services, or workloads—flows through identity verification and authorization."
IaC Security Implementation
Complete Terraform examples for deploying secure cloud infrastructure with automated compliance checks and policy enforcement.
"Infrastructure as Code must be treated as any other production code: scanned, tested, reviewed, and enforced through automated guardrails in CI/CD pipelines."
Multi-Cloud Federated Identity
Step-by-step guide for implementing unified identity across AWS, Azure, and GCP with practical examples and troubleshooting.
"Federated identity removes the need to sync passwords and secrets across clouds. Instead, a central identity provider issues short-lived credentials."
Get instant access to all 18 chapters with code examples, architecture diagrams, configuration templates, and real-world implementation strategies.
Plus 5 hands-on labs (Appendix A) and a comprehensive glossary of cloud security terminology.
Why Architects Choose This Handbook
Designed for practitioners who need actionable knowledge, not just theory
Real-World Architectures
Battle-tested patterns extracted from securing multi-cloud platforms serving millions of users. Not theoretical exercises.
Immediate Implementation
Code examples, IaC templates, and deployment strategies you can copy into your environment today.
Future-Proof Coverage
From foundational Zero Trust to emerging threats like AI security and post-quantum cryptography.
Business-Aligned Security
Learn to measure security ROI, optimize costs, and demonstrate value to business stakeholders.
Multi-Role Relevant
Designed for CISOs, architects, engineers, and security practitioners at all experience levels.
5 Practical Labs Included
Five deployable labs: Zero-Trust VPC, DevSecOps Pipeline, AWS Identity Center SSO, GuardDuty alerting, and S3 encryption enforcement with AWS Config.
This handbook is designed to sit on your desk (or in your browser tabs) as you actually build and operate cloud infrastructure.
Every chapter has been optimized for practical reference, with quick lookups, architecture patterns, and implementation strategies you can apply immediately to solve real-world security challenges.
Frequently Asked Questions
Everything you need to know about the handbook
Yes! The handbook starts with foundational concepts like the shared responsibility model and Zero Trust principles. Part I covers the essentials, and it's structured so you can learn progressively. However, it also goes deep into advanced patterns, making it valuable for experienced architects too.
Still have questions? Reach out to us for more information.
We're here to help you get the most out of this handbook.
Meet the Author
Battle-tested expertise from years of securing enterprise cloud platforms.
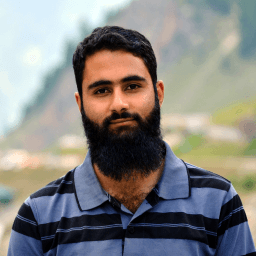
Afaan Bilal is a Principal Software Engineer and CISO with over 12 years of experience securing cloud platforms at scale. He has led SOC 2 Type II and ISO 27001 certification programs and built security teams from the ground up.
Throughout his career, Afaan has designed and implemented secure cloud environments combining theoretical rigor with practical implementation strategies that balance security, reliability, and cost efficiency.
"This handbook represents years of lessons learned. It's the guide I wish I had when I started."
Core Competencies
18 Chapters
Comprehensive Coverage
150+ Pages
In-Depth Content
12 Tables
Decision Reference
5 Labs
Hands-On Practice
The Reference Practitioners Actually Keep Open
Covers Zero Trust networking, IaC supply chain security, Kubernetes Pod Security Standards, OAuth 2.1 / PKCE, SPIFFE/SPIRE workload identity, SOAR automation, AWS GuardDuty, Terraform security, GraphQL API security, and post-quantum cryptography readiness — structured as a reference you return to, not a book you read once.
7-day money-back guarantee. No questions asked.